Trending Topics

 Trending
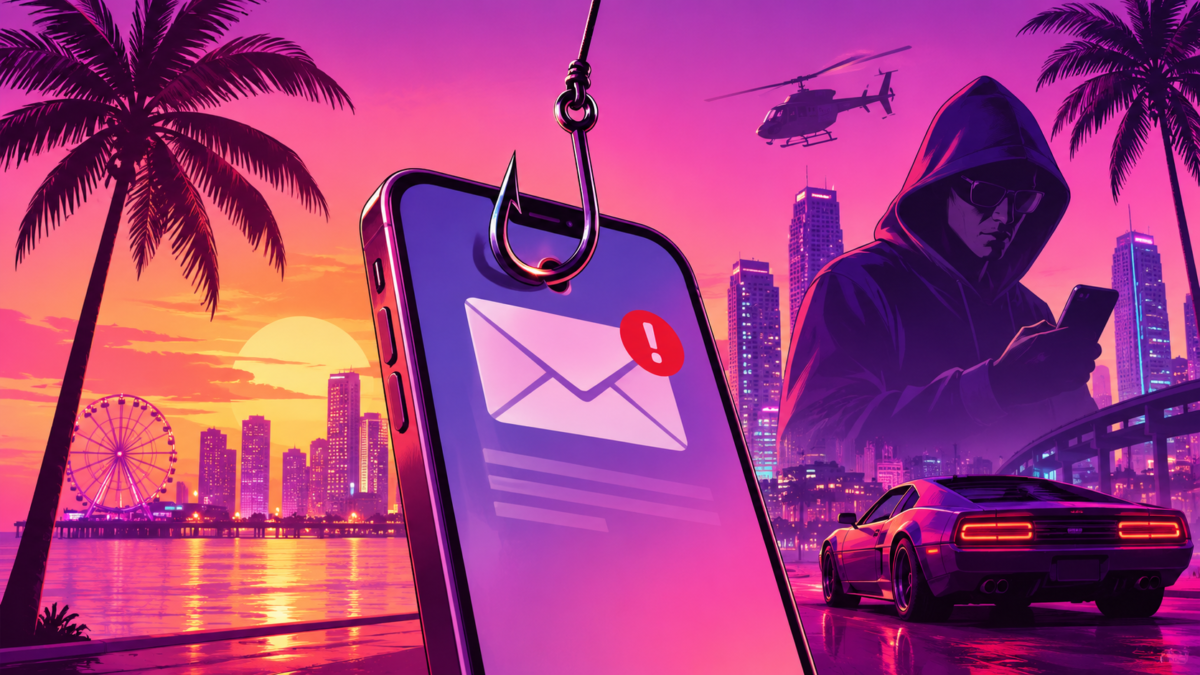
GTA 6 launch hype drives 1,300% surge in gaming phishing

Cybercriminals used anticipation surrounding the release of highly-anticipated Grand Theft Auto 6 (GTA 6) to drive a 1,300% increase in gaming-related phishing emails between March and August 2026, with campaigns targeting both consumers and corporate employees, according to security company KnowBe4.
Data from KnowBe4’s Threat Lab found that while GTA-themed phishing accounted for just 0.005% of threats in September, the week beginning October 26 saw GTA-related lures accounted for 9.6% of all phishing volume.
According to Knowbe4, the campaigns took two forms: mass-market scams promoting fake rewards and targeted attacks impersonating employee benefits programmes.
Recommended reading: Prepare your defences: Grand Theft Auto VI has finally arrived and enterprises are under attack
Consumer scams and targeted corporate attacks
Consumer-facing campaigns used blank emails containing a single link, which directed recipients to fraudulent websites styled around GTA 6 and Rockstar Games. The pages advertised a fictitious $4,000 bonus using the promotional code ‘ROCKSTAR’, before redirecting victims to online casinos or cryptocurrency platforms to collect passwords, payment card details and cryptocurrency deposits.
The campaigns averaged 84 attacks each, with the United States and United Kingdom accounting for 47% and 35% of activity respectively. Education, technology and finance were the most targeted sectors.
A second wave targeted corporate employees with fake offers for free GTA 6 pre-orders, supposedly provided through corporate employee benefits programs. The messages used artificial deadlines and limited availability claims to encourage employees to click links.
KnowBe4 found that 83% of this attack activity occurred on weekends, when employees were more likely to check work emails for personal offers. During the October 31 to November 1 weekend, GTA-related impersonations accounted for 42% of all phishing emails processed.
Evasion techniques and technical manipulation
“To ensure these targeted corporate lures bypass perimeter defences, attackers combine psychological manipulation with a multi-layered technical evasion strategy,” KnowBe4 said.
“Rather than spoofing existing brands, threat actors register look-alike vendor domains that allow their emails to cleanly pass SPF, DKIM, and DMARC authentication checks. Once inside the inbox, the messages evade traditional image-based scanners by rendering QR codes entirely out of Unicode text block characters or HTML tables.”
Recommendations for mitigation
The company recommends that organisations educate employees about phishing attempts disguised as HR benefits and other workplace offers, particularly those sent outside business hours. It also advises establishing clear processes for communicating legitimate employee benefits through internal HR portals or intranets.
Organisations should also ensure email security systems can identify QR codes embedded in text or HTML, and remind employees to treat unsolicited links and requests to scan codes with caution, KnowBe4 said.
Recommended reading
About The Author
Aimee Chanthadavong
NEXT UP