Trending Topics

 Trending
Cisco brings Claude Mythos to AI Defense to stress-test enterprise agents

Giving AI agents access to business systems raises a difficult question: how do you find their vulnerabilities before an attacker does? Especially now, when attackers have capabilities they didn’t have before, like turning overlooked software bugs into workable attacks. At Cisco Live Melbourne 2026, Cisco announced it is adding Anthropic’s Claude Mythos to AI Defense to help security teams test those agents against more sophisticated attacks.
During the “Lead in the Agentic Era” keynote, Jeff Schultz, Cisco’s senior vice president of portfolio strategy and marketing, stressed the need to consider “red teaming agents, not just models”. He explained that AI Defense would use Mythos internally to reason about ways to attack deployed agents and models.
The readiness gap is substantial.
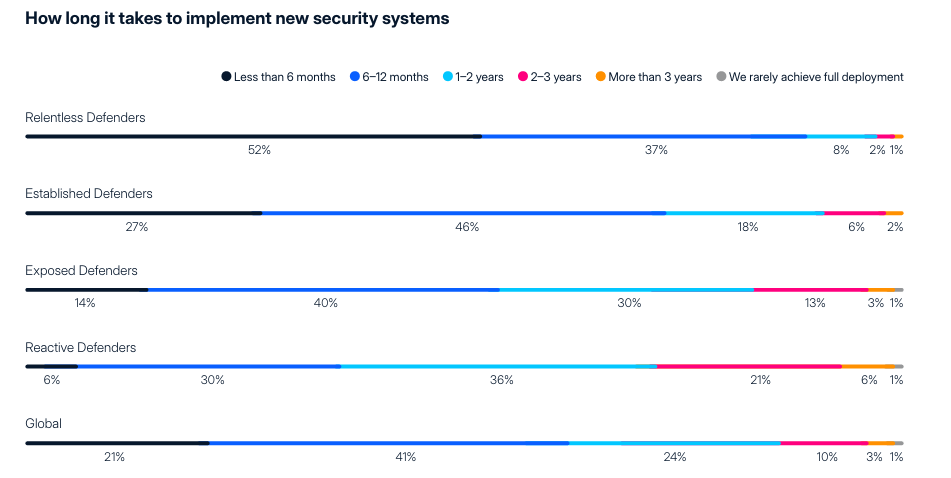
Earlier in the keynote, Cisco’s APJC president Ben Dawson said only 52% of respondents across the region were confident they could detect and respond to compromised AI agents, according to Cisco’s Relentless Defense Report 2026.
Testing agents, not just models
Cisco’s existing adaptive red teaming builds customised, multi-step attacks to uncover weaknesses in AI systems. Mythos will augment that framework with reasoning that plans tests and generates attack ideas specific to each system, according to the accompanying announcement.
As we explored in our recent coverage of AI agents’ spending, access and oversight, completing an assignment does not necessarily mean an agent acted appropriately. Testing needs to examine the route it takes, not merely the answer it produces.
The testing tool needs boundaries
Cisco says customers will not receive unrestricted access to prompt Mythos. Tests will run only against customer-owned, registered and authorised targets, with each engagement tied to a named operator, recorded for audit and stoppable on demand.
Those controls address the testing process, not every risk of deploying agents. As our examination of cybersecurity’s struggle to keep pace with AI adoption highlighted, pre-deployment checks must sit alongside access governance and runtime protection.
Mythos-enabled adaptive red teaming is coming soon for select enterprises, rather than generally available, and Cisco says release timelines remain subject to change.
More realistic attacks could expose weaknesses that simpler tests miss. The practical question is whether customers can turn those findings into fixes.
About The Author