Trending Topics

 Trending
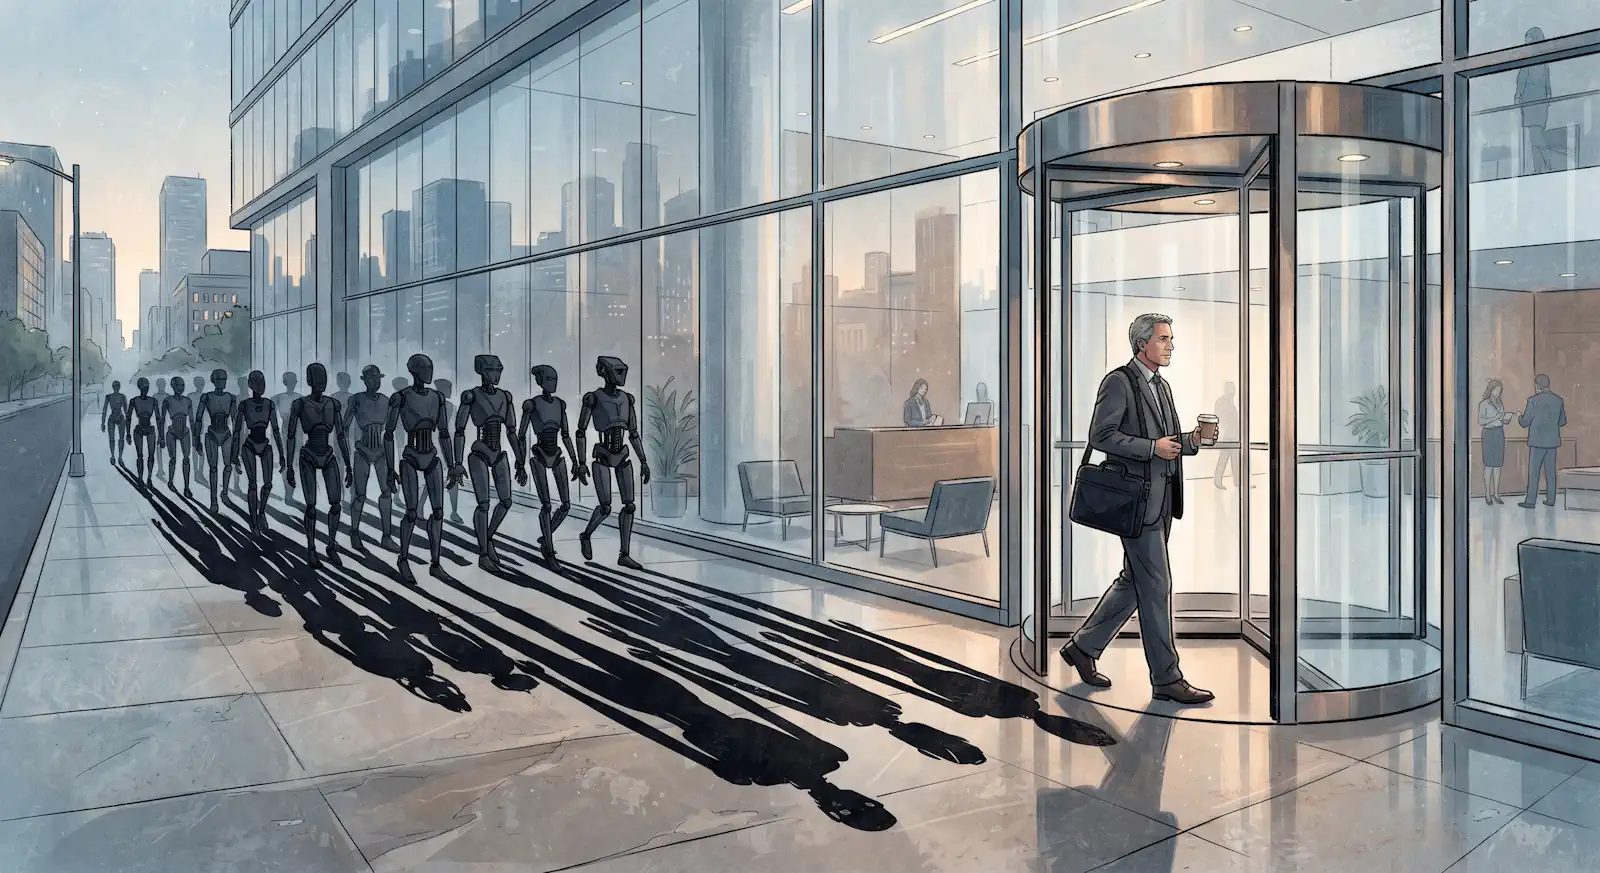
The AI agents your employees hired without telling IT

AI agents are finding their way into businesses without IT knowing. As they gain access to corporate systems and sensitive data, how can organisations keep them under control?
Staff using ChatGPT without permission was already enough to keep IT departments busy, but now employees can set up AI agents that don’t just produce answers but actually do things, from replying to customer emails to making changes in company databases.
These agents need access to corporate systems to do any of that, and employees setting them up themselves may be granting far more permissions than necessary, without IT knowing what’s been authorised.
Staff are taking AI into their own hands
The enthusiasm for AI at work is proving difficult for employers to contain. Research from the British Standards Institution (BSI) found that 42% of people use AI tools their organisation hasn’t approved, while just 37% said their employer controls how staff use the technology.
More than half of respondents (55%) also said they believe the productivity benefits of AI are worth the risk of data and security breaches.
Those figures aren’t specific to autonomous agents, but they show how willing employees are to experiment with AI without necessarily involving the people responsible for security.
“Shadow AI is already widespread and poses a major risk to organisations across the world,” Omkar Joshi, Managing Director for AI and Digital Solutions at BSI, told TechFinitive.
SailPoint estimates that 79% of organisations are already using AI agents in production. However, only 2% have introduced identity security tools designed specifically for them, even though agents now make up 22% of non-human accounts, according to the company’s research.
For IT teams, every new agent brings more credentials and access rights to track. Some may have been set up by employees without approval, with permissions that go well beyond what the agent actually needs. And unless someone is checking, those permissions could remain in place long after the original task is finished.
The permissions problem
An AI agent handling customer enquiries could need access to the company’s CRM system, but there’s a difference between letting it look up customer details and giving it permission to edit records, extract sensitive information or send emails. An employee keen to get the thing working might not be too concerned about that.
And those permissions don’t necessarily disappear when the agent has finished its original task.
“Agents connected to corporate systems can expose confidential data, misuse inherited permissions or take unintended actions across multiple applications,” Joshi warns.
Anyone who gets hold of an agent’s API key could inherit its permissions, potentially giving them access to sensitive records or the ability to change them. There’s also the risk of the agent making a mess of things on its own, particularly if it takes an instruction too literally or gets the wrong end of the stick.
And it won’t necessarily wait around for someone to notice. An agent could work its way through hundreds of records or carry out a string of actions in the time it takes an employee to realise something’s gone wrong.
The employee leaves. The agent stays.
Businesses generally know what to do when an employee leaves. Their accounts are disabled, access is revoked, and their laptop is collected.
But what happens to the AI agent they created to automate their monthly reporting?
Leaving the company doesn’t necessarily mean an employee’s AI agents leave with them. Some have their own API tokens or service accounts, which can remain active even after the employee’s login has been disabled.
“An agent can become an ‘orphaned’ digital identity, continuing to access information, use credentials or trigger workflows after its creator has left,” Joshi explains.
To avoid this, Joshi says every agent should have a named owner, with its access reassessed when that person changes roles or leaves.
That requires businesses to know which agents exist in the first place. SailPoint’s research found that just 39% of organisations currently have governance arrangements in place for AI agents.
Wendy Wu, Chief Marketing Officer at SailPoint, argues that the usual approach to managing employee access isn’t going to be sufficient.
“You cannot bridge this gap by asking human-speed tools to work faster; security must be built for machine speed from the ground up, with discovery, ownership, and access decisions happening in real time rather than on a quarterly review cycle.”
Getting the agents back under control
AI agents aren’t always easy to spot, particularly when they’re running through browser extensions, developer tools, or cloud services. Even after tracking them down, IT still has to establish which credentials they’re using, what systems they can access, and whether those permissions have ever been reviewed.
SailPoint’s Agentic Fabric solution brief looks at how companies can track down these agents, establish who owns them, and see which systems and data they’re able to access. It also covers monitoring their activity and cutting off access when necessary.
“Traditional identity and access management tools remain essential, but they were generally designed around human and conventional machine identities, not agents that dynamically plan and act,” says Joshi.
Joshi isn’t calling for a ban. He wants companies to know what their agents are doing, cut back unnecessary permissions and insist on human approval for sensitive tasks. With employees already ignoring the rules on AI, another blanket ban could prove difficult to enforce.
“Organisations should provide approved alternatives, establish a simple agent-registration process and apply proportionate controls based on data sensitivity and autonomy,” Joshi advises.
An agent that’s been identified, assigned an owner and given appropriate permissions may be perfectly safe to keep running. One that presents an immediate security risk needs to be stopped, with its access revoked.
Employees are unlikely to stop experimenting with AI agents simply because IT would prefer them to ask permission first. Businesses therefore need a way to bring those agents into the fold, rather than pretend they aren’t there.
After all, it’s difficult enough keeping track of the people who work for a company without having to worry about the software they’ve quietly recruited to help them.
Related articles
About The Author