Trending Topics

 Trending
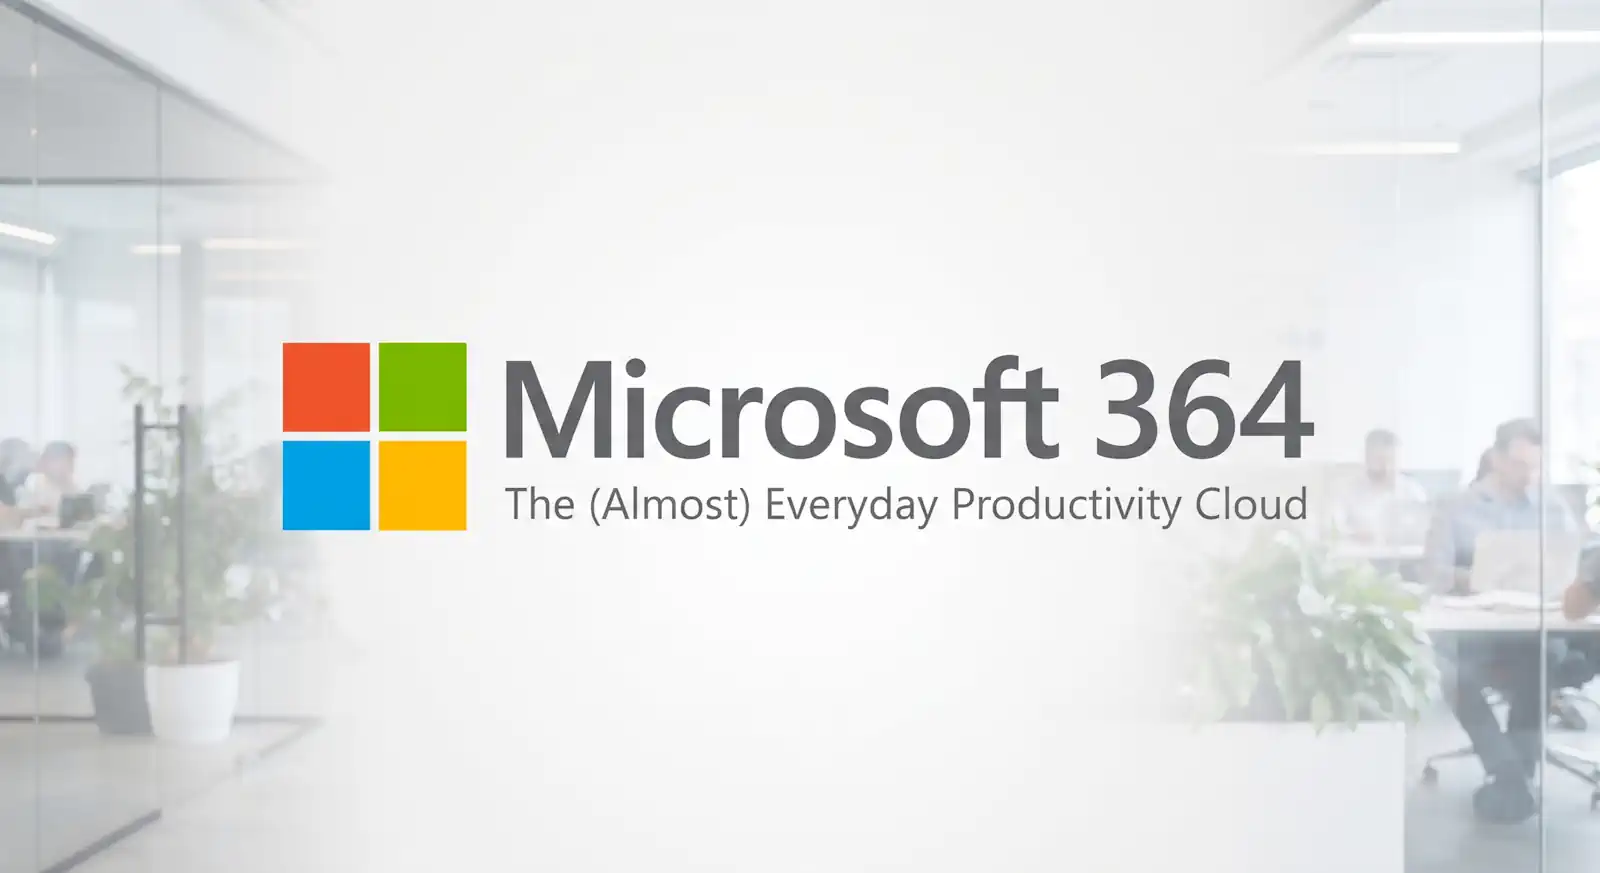
Microsoft 365 is down! What now? And what’s next?

Microsoft 365 is down and the company has so far been unable to fix it.
That means many have been left unable to check email, link up with colleagues on Teams, or complete any of the other tasks we’d normally dread on a Friday afternoon.
As Microsoft works to regain services – and IT departments struggle to keep companies running – here’s what you need to know about the incident and what to do next.
What happened to Microsoft 365?
Thursday morning in California – about 6pm in the UK – issues started to crop up with various parts of Microsoft 365, which includes Excel, Outlook and Teams, among other services. At the time of writing, the outage was still ongoing, nearly two full days later. The incident is impacting services globally at this point.
Microsoft has said the outage doesn’t appear to be security related; this morning it said it likely centred on a configuration update related to Microsoft Exchange. When Microsoft addressed that issue, servers were overloaded with traffic.
As of lunchtime in the UK, Microsoft said it was seeing “continued recovery progress across affected regions”, though added that some users may continue to see “intermittent access issues or delayed email delivery” in some areas.
Given the widespread usage of Microsoft, organisations from government agencies such as the NHS in the UK down to small businesses have been impacted, including OpenAI and Anthropic.
Prof Dimitrios Pezaros, Director of the University of Glasgow’s Cyberdefence Lab, said in a statement that these incidents “demonstrate how a single faulty software update can cascade across thousands of organisations and disrupt critical services, including healthcare, transport and financial systems”.
Now what?
Anyone reliant wholly on Microsoft should perhaps take Friday off. Online commenters have said the tech giant should rename its product suite Microsoft 364, or perhaps if this carries on, Microsoft 363.
“With no emails coming or going, many office workers feel like they are having a virtual snow day,” said Jeremy Singer, Professor of Computer Systems and Programming Languages at the University of Glasgow’s School of Computing Science.
But one expert called for caution when it comes to workarounds, as staff look for alternative tools that may not be secure.
“When things like this Microsoft outage happen, people immediately start looking for workarounds just to keep things moving, and that means switching to tools and systems that aren’t the ones normally used or approved by organisations,” said Associate Professor Micheal Axelsen, Senior Lecturer for the UQ Business School at The University of Queensland.
“Organisations need to be careful with what people are doing now, when their usual systems are down, and what tools and programs people are using, as that introduces a potential risk.”
What next for Microsoft 365?
Simon Azzopardi, CEO of CoreView, suggested it’s not time to take a day off, but to prepare for recovery.
“As services recover, IT teams should do three things,” he said in a statement. “Confirm that security and compliance controls such as data loss prevention, sensitivity labelling and Intune compliance policies are working as intended. Review every emergency change made during the outage, because workarounds made under pressure tend to become permanent gaps. And treat delayed email with extra caution: Microsoft warned that Safe Links might not be able to check URLs during the disruption, and attackers routinely use outages as cover.”
And if you’re not on the IT team, perhaps be ready with a coffee, pint or whatever else is required. “Our sympathy goes out to every IT team that has spent their time keeping their organisation running without email, calendars and, in many cases, their security and compliance tools,” Azzopardi added.
After recovery
Post recovery – whenever that will be – companies that rely on Microsoft or any other major tech supplier need to rethink their resilience plans.
Steven Watt, Professor of Practice in Cybersecurity at the University of St Andrews, said organisations should be able to answer a few basic questions: “Which of our critical processes depend on a single supplier? How long could we operate if that supplier were unavailable? What is our fallback for communicating with staff, customers and regulators? Have we tested it, or do we simply assume it exists?”
Glasgow’s Pezaros agreed that diversity in supply chains can help build resilience. “By adopting multi-vendor strategies, organisations can reduce their dependence on just a handful of providers and minimise the risk of a common infrastructure failure disrupting critical services,” he added.
Watt added that none of this necessarily means ditching Microsoft or other cloud companies. “The aim should be strategic autonomy which is keeping enough choice, portability and operational capability that dependence on any single provider does not become an unacceptable risk,” Watt said.
This might be a Microsoft outage, but like massive incidents before it – such as CrowdStrike in 2024 – it’s very clear that over reliance on one tech vendor is becoming a problem for all of us.
Related articles
About The Author
Nicole Kobie
NEXT UP