Trending Topics

 Trending
Europe’s supermarket fridge attacks expose growing risks to connected infrastructure

A series of cyberattacks targeting supermarket refrigeration systems across Europe has highlighted how vulnerabilities in connected operational technology can cause significant physical and financial damage, even without the theft of data or deployment of ransomware.
Following incidents affecting supermarkets in France, Belgium, Sweden, Luxembourg, Estonia and Ireland, cybersecurity experts are warning that poorly secured refrigeration controllers and remotely accessible industrial equipment are creating opportunities for attackers to disrupt essential services.
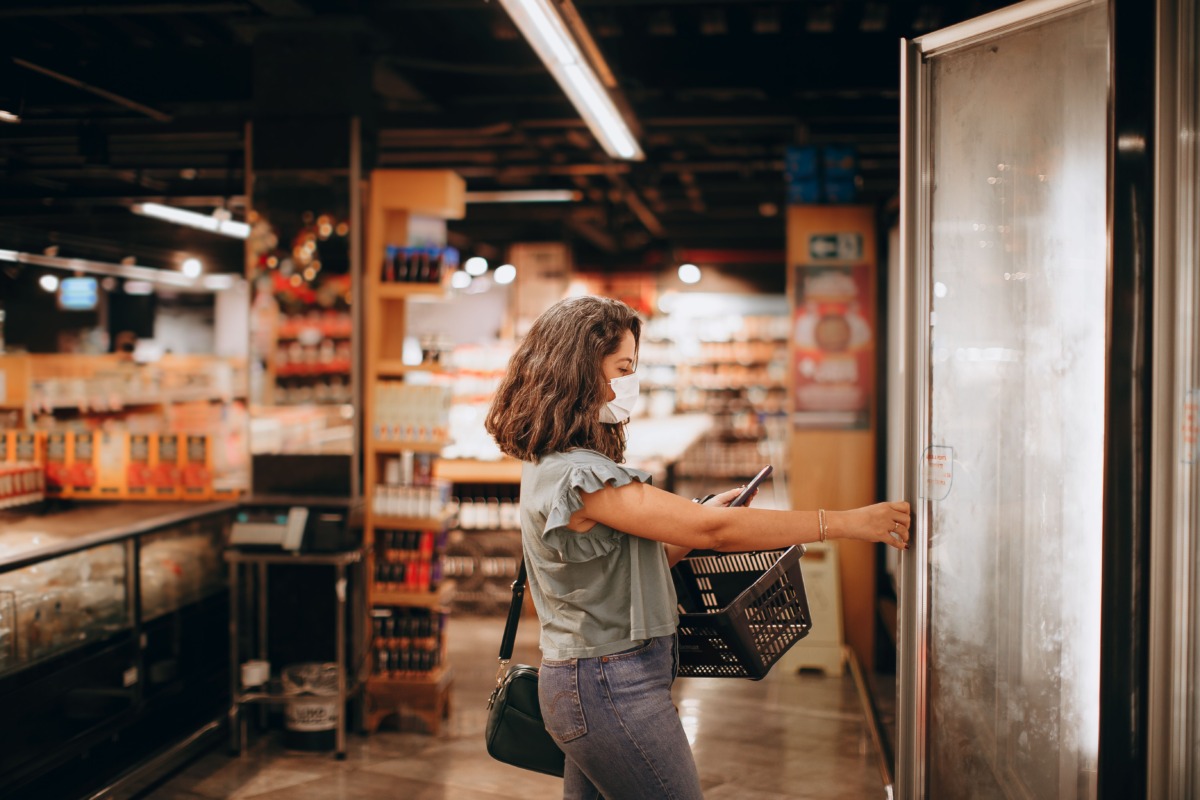
The attacks have reportedly involved manipulating refrigeration units, including forcing them into defrost cycles, causing stock to spoil and stores to close. For Martin Riley, CTO at UK critical national infrastructure cybersecurity specialist Bridewell, the incidents represent a shift in how attackers are targeting the food and drink sector.
“In most of IT security we protect confidentiality first. We worry about data being stolen. In operational technology that priority flips. Availability and integrity come first, because the process has to keep running and keep running correctly,” he explained.
A supermarket refrigerator might not contain sensitive information, but changing its temperature overnight can destroy the value of everything inside it within hours. Unlike compromised data, spoiled stock cannot simply be restored from a backup.
Why refrigeration systems are becoming attractive targets
Riley believes the food and drink industry presents an appealing combination of vulnerabilities for attackers: perishable products, thin margins and operations that depend on tight schedules.
The sector is also highly distributed, with retailers, manufacturers and distributors relying on equipment spread across hundreds of sites. Much of this infrastructure is maintained by specialist contractors and connected to the internet to enable remote monitoring and management.
That convenience, however, has created a sizeable attack surface.
Bridewell’s analysis identified more than 6,000 refrigeration management panels from a single manufacturer visible on the public internet worldwide. In the UK, more than 800 refrigeration and building-control interfaces have reportedly been identified as reachable online.
Some of these systems were never designed to be directly exposed to the internet, while others are running end-of-life controllers that no longer receive security updates.
The problem is compounded by the relative simplicity of the attacks. Riley said vulnerabilities in refrigeration controllers had been publicly disclosed in August, with fixes available, but many systems remained exposed. Research also demonstrated that an AI coding agent could reproduce known exploits for one of the controllers in approximately 28 minutes, at a cost of around $6.
Patrick Lamplmair, CTO and co-founder of Tributech, believes the speed at which the incidents have spread demonstrates that attackers have found a method that works.
“Three weeks after France, supermarkets in Belgium and Sweden have been hit in the same way. This is no longer a one-off incident. It is a method that works, and attackers will keep using it until it stops working,” he said.
Lamplmair added that the attacks are relatively inexpensive to execute but can have immediate consequences, with a single compromised controller potentially affecting hundreds of sites.
The risks extend beyond supermarkets
Although retailers have attracted the headlines, the vulnerabilities are not exclusive to supermarket refrigeration systems.
Manufacturers, food producers and distributors rely on similar remotely managed equipment, including cold stores, industrial refrigeration plants, production lines and packaging systems.
Riley warned that the impact can travel well beyond the initial victim. Manufacturers lose stock and orders, farmers and growers can see products written off, while refrigeration contractors may face reputational damage and remediation costs.
Ultimately, consumers can also bear the consequences through reduced availability, higher prices and disruption to local food supplies.
He argued that food should be considered critical infrastructure, given the potential for coordinated attacks to spoil products across multiple countries in a single night.
James Stanley, Head of Engineering at WITTENSTEIN High Integrity Systems, similarly warned that the incidents expose weaknesses in the wider ecosystem of connected products.
“The latest attack on supermarket fridge systems in Belgium comes less than a month after French supermarkets were hit by a similar incident. While supermarket fridges might seem an unusual target, they are connected to wider systems that help stores operate, making them an attractive weak spot for attackers,” he said.
For Stanley, the problem is partly rooted in how manufacturers approach product security. Embedded systems are often designed to operate for years, but security support and vulnerability management do not always receive the same long-term consideration.
He believes manufacturers must think about security throughout the entire lifecycle of connected products, while buyers should be asking suppliers how long equipment will receive support and how newly discovered vulnerabilities will be addressed.
The EU’s Cyber Resilience Act is intended to address some of these shortcomings, introducing requirements around secure-by-design development and vulnerability handling throughout a product’s declared support period.
Moving beyond basic security measures
The immediate response, according to the experts, starts with reducing the number of systems exposed to the internet.
Riley recommends that organisations continuously identify externally accessible operational technology, remove direct internet access to refrigeration controllers and route remote connections through secure gateways protected by multi-factor authentication.
Third-party contractors and original equipment manufacturers must also be treated as part of the organisation’s attack surface, with remote access named, time-limited and logged. Equipment that can no longer receive security updates should be isolated and placed on a funded replacement programme.
However, Lamplmair believes conventional network security and patching will only go so far.
“The lasting fix is to stop trusting the network and verify at the asset itself,” he said.
He argued that commands sent to industrial equipment should have their origins verified and be checked for tampering before execution. Setpoints should also be validated against physical limits, preventing a refrigeration unit from accepting an instruction that would put its operation outside safe parameters.
“This must be designed in from the start, not added later,” he added, pointing to the EU Cyber Resilience Act as an important driver of greater manufacturer accountability.
Stanley also stressed that regulation alone will not prevent future incidents. Security and long-term support need to become central considerations when connected products are designed, purchased and deployed.
For Riley, the lesson is that organisations need to broaden their understanding of what a successful cyberattack looks like.
“For twenty years the industry has worried about attackers stealing data. These attacks show they are now willing to spoil the milk.”
The immediate damage may be measured in spoiled stock and empty supermarket shelves. But the wider warning is that any connected physical asset with inadequate security could become the next target.
You might also be interested
- Abnormal AI warns that AI agents need a stopping rule, not just access controls
- Unexpected AI bills and rising telemetry costs challenge enterprises, Cisco study finds
- BT International and Netskope fuse network and security for the AI era
- What experts are saying about the ASOS hack – immediate lessons for ASOS customers and all businesses
About The Author